← CTF HUB/DEADFACE CTF 2026 // OPERATIONAL DOSSIER

DEADFACE CTF

Complete technical writeups across Network Traffic Analysis, Volatility 3 Memory Forensics, Chrome SQLite Artifacts, Aurora Health Database SQL, Savannah OSINT, and LLMNR/SMB Poisoning.

● 20 Core CTF Challenges
● 25 Verified Flags Extracted
● Exact Commands & SQL Queries
● Downloadable Artifacts Included
DEADFACE CTF Banner
Category 01

Traffic Analysis & Network Forensics

Traffic Analysis // DNS Tunneling & HTTP Staging100 PTS

1. Bad Guys Be Bad

Trace suspicious network activity, locate an external staging configuration, and recover the secret exfiltrated by DEADFACE.

SOURCE ARTIFACTFolder: C:\CTFS\DEAD FACE CTF\1\
Download deadface_pcap02.pcap (63.2 KB)

Retrace / Steps:

1. Opened deadface_pcap02.pcap in Wireshark.

2. Discovered HTTP Staging & Secret XOR Key:

Filtered for the staging server connection:

ip.addr == 45.13.37.7 && tcp.port == 8080

Followed the TCP stream on the GET /staging.bin request and guess what The server returned the attacker's staging config:
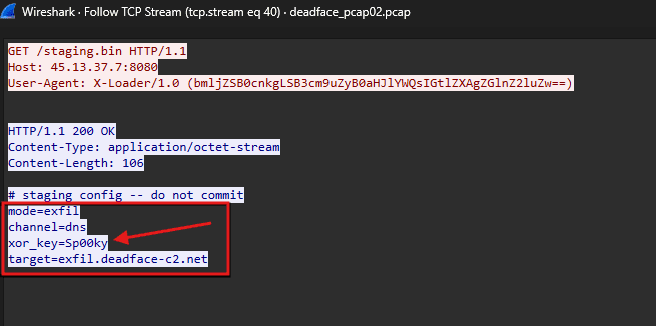
Wireshark TCP Stream showing staging.bin configuration
mode=exfil
channel=dns
xor_key=Sp00ky
target=exfil.deadface-c2

This showed that data was being smuggled out over DNS using the repeating XOR key Sp00ky surprised? yeah me too ( u alone )

3. Collected Exfiltrated DNS Chunks:

Filtered Wireshark for the tunneling domain:

dns.qry.name contains "exfil.deadface-c2.net"

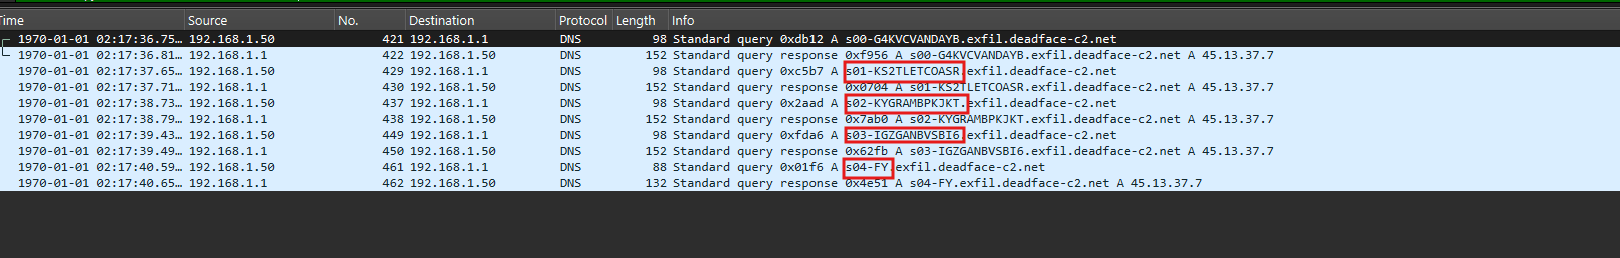
Extracted the ordered query subdomains (s00 through s04):

s00-G4KVCVANDAYB
s01-KS2TLETCOASR
s02-KYGRAMBPKJKT
s03-IGZGANBVSBI6
s04-FY

Stripped the s00- prefixes and joined the Base32 chunks in sequence:

G4KVCVANDAYBKS2TLETCOASRKYGRAMBPKJKTIGZGANBVSBI6FY

intersting right?

DNS Query Subdomains in Wireshark

4. Decoded Flag in CyberChef:

Pasted the concatenated string into CyberChef with this recipe:

  1. From Base32
  2. XOR (Key: Sp00ky, UTF8)

Output decoded directly into the flag:
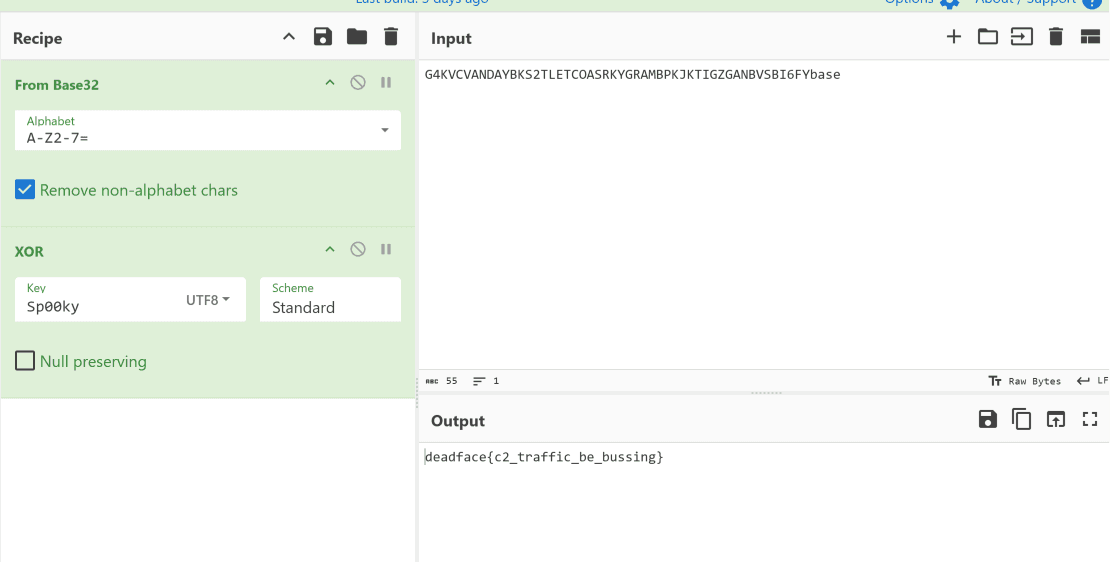
CyberChef Base32 and XOR Decode
Captured Flagdeadface{c2_traffic_be_bussing}easy right ? ;0
Traffic Analysis // Covert Exfil150 PTS

2. Data Go Brrrrr

Detect high-volume exfiltration concealed inside an unexpected protocol.

SOURCE ARTIFACTFolder: C:\CTFS\DEAD FACE CTF\Data Go Brrrrr\
Download PCAP01.pcap (2.9 KB)

Retrace / Steps:

1. Identified ICMP Traffic Anomaly:

Filtered PCAP01.pcap for ICMP packets:

icmp

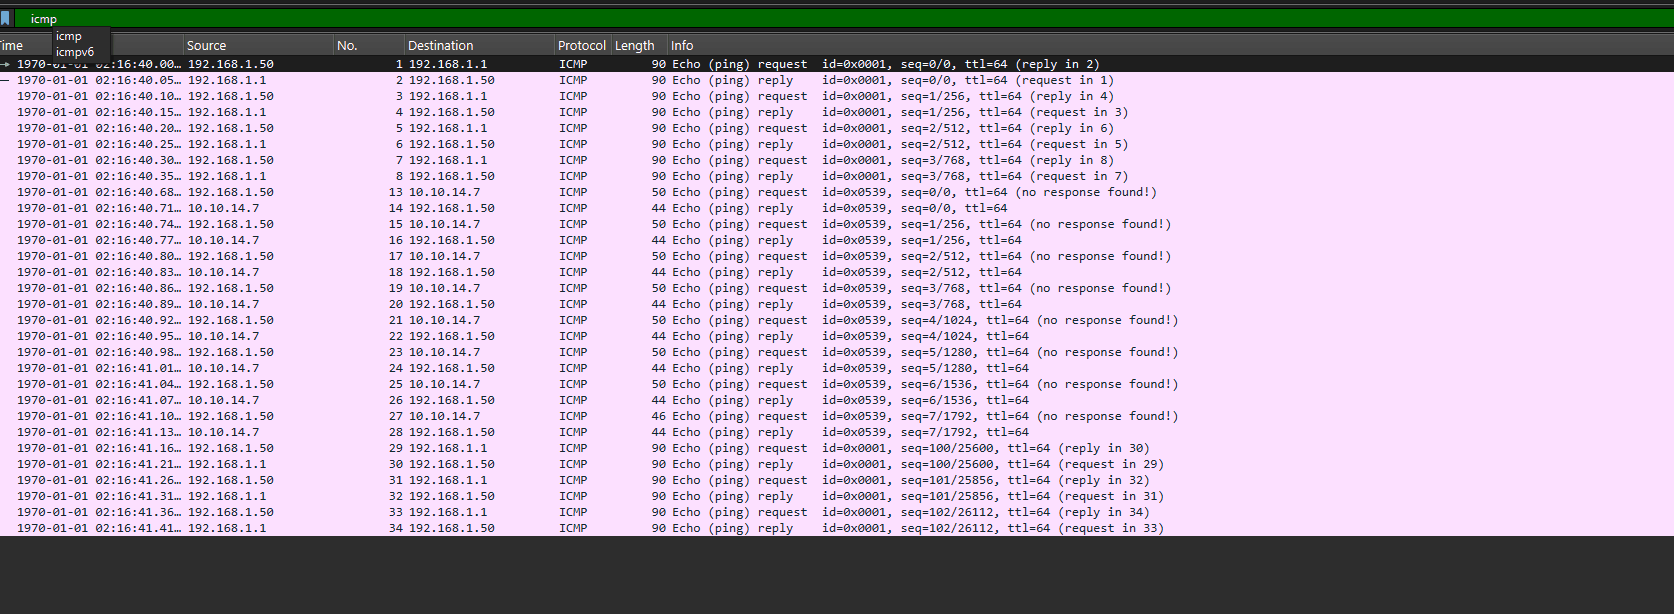
Baseline traffic showed standard 90-byte pings to the gateway 192.168.1.1. However, a burst of 50-byte requests appeared targeting an external host 10.10.14.7:

soo guess what !

Wireshark ICMP Echo Request burst targeting 10.10.14.7

u guessed??

2. Isolated Exfiltration Requests: ( hope u think of that too )

Filtered specifically for the outbound packets to the suspect IP:

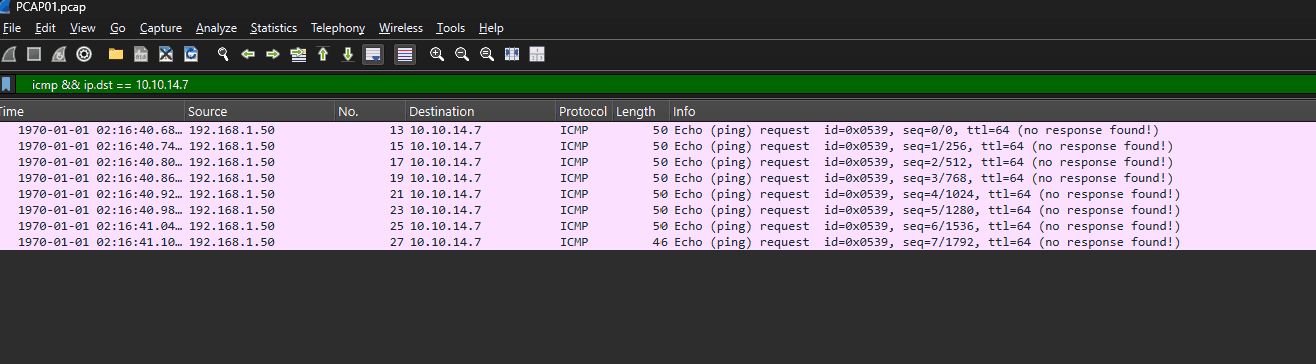
icmp && ip.dst == 10.10.14.7

This isolated 8 distinct Echo Requests (Packets 13, 15, 17, 19, 21, 23, 25, 27):

Filtered ICMP Echo Requests 13 through 27

3. Inspected Payload Data (Base64 Chunks):

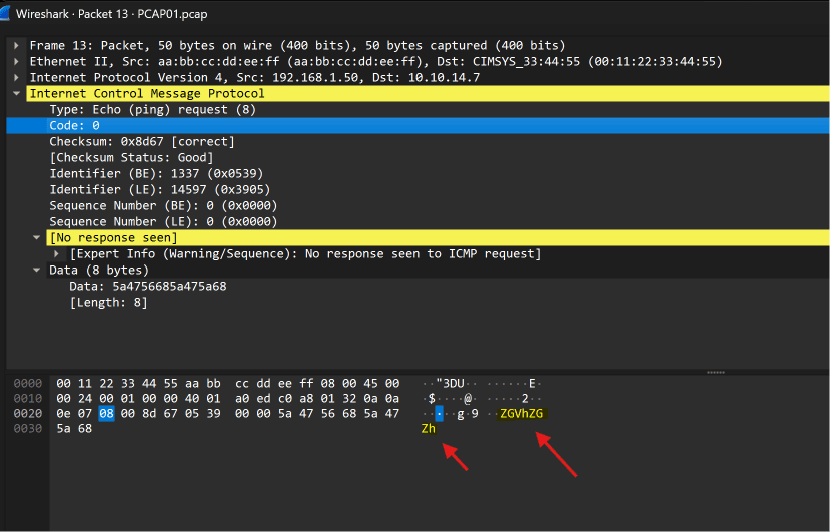
Selected Packet 13 and expanded the ICMP data field (Data (8 bytes)). Instead of default ping padding, the payload contained custom ASCII characters ZGVhZGZh:

ICMP Payload custom ASCII bytes

guess what :) there's more

Checking each outbound request revealed sequential 8-byte Base64 chunks:

PacketHex DataASCII (Base64 Chunk)
Packet 135a4756685a475a68ZGVhZGZh
Packet 155932563761574e74Y2V7aWNt
Packet 176346387a65475a70cF8zeGZp
Packet 196246393361444e75bF93aDNu
Packet 215833526f4d336c66X3RoM3lf
Packet 236247566863335266bGVhc3Rf
Packet 256333567a63444e6ac3VzcDNj
Packet 276448303ddH0=

4. Reassembled & Decoded in CyberChef:

Concatenated the chunks into the full Base64 string:

ZGVhZGZhY2V7aWNtcF8zeGZpbF93aDNuX3RoM3lfbGVhc3Rfc3VzcDNjdH0=

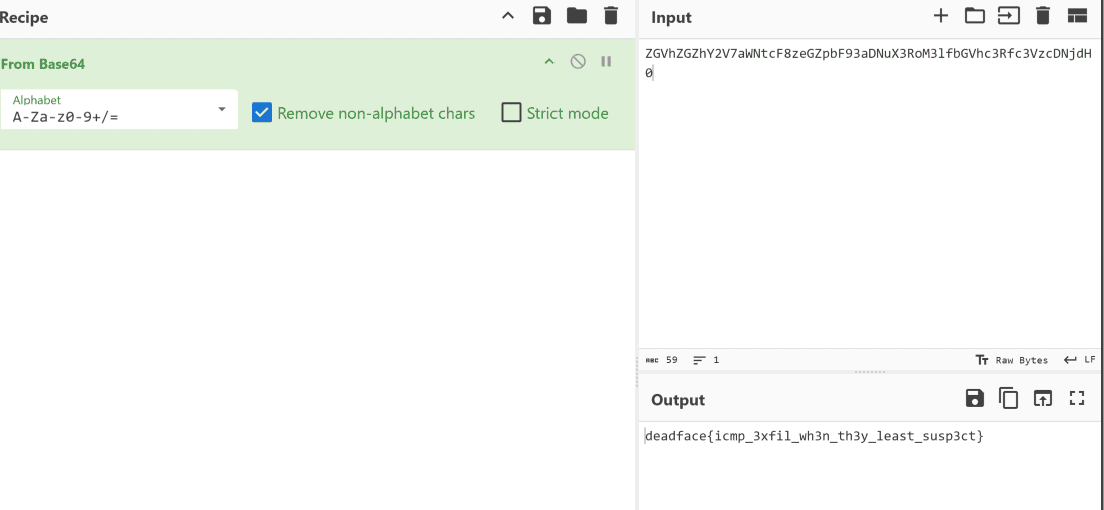
Decoded using the From Base64 recipe to recover the flag:

CyberChef Base64 Decode output
Captured Flagdeadface{icmp_3xfil_wh3n_th3y_least_susp3ct}it was good not easy or easy idk u decide 0;
Traffic Analysis // VoIP & Audio250 PTS

3. Don't Leave Me Hanging ( listen to him its long challenge)

Investigate anomalous help desk telephony traffic, bypass SRTP stream encryption, and recover secret in-band audio tones.

SOURCE ARTIFACTSFolder: C:\CTFS\DEAD FACE CTF\Don't Leave Me Hanging\
pbx-diag-20261008.tar.gzDontLeaveMeHanging.pcap (83 MB Local)

Retrace / Steps:

1. Intercepted PBX Diagnostics via FTP:

Filtered DontLeaveMeHanging.pcap for FTP file transfers:

ftp || ftp-data

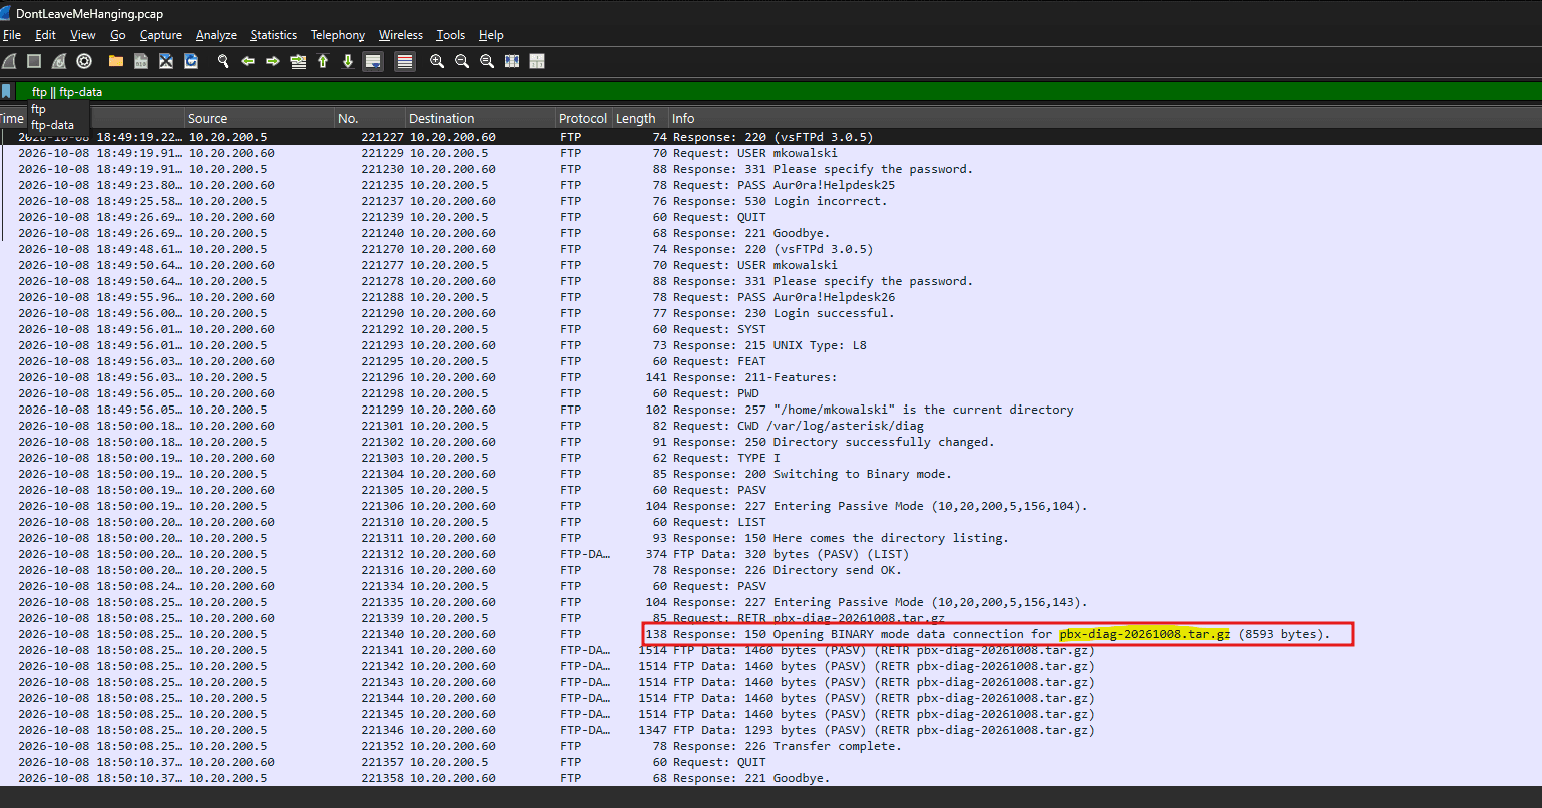
Identified user mkowalski downloading the PBX diagnostic archive pbx-diag-20261008.tar.gz from the PBX server (10.20.200.5):

Wireshark FTP file transfer analysis

2. Analyzed PBX Logs & Discovered In-Band Audio Anomaly:

Extracted the archive to inspect the Asterisk PBX logs (messages.log) and SSL secrets (tls-keys.log).

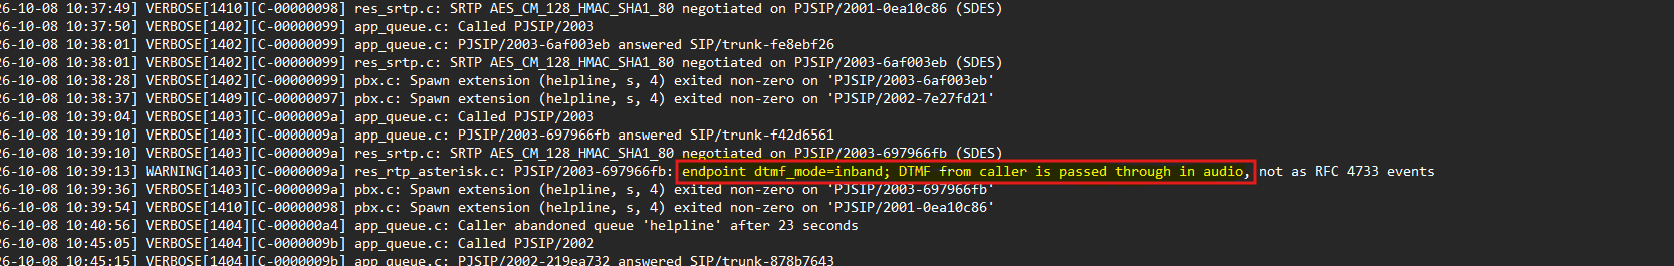
Standard VoIP systems transmit dial tones as out-of-band network events (RFC 4733). However, a critical warning in messages.log revealed that extension 2003 was misconfigured:

WARNING: PJSIP/2003-697966fb: endpoint dtmf_mode=inband; DTMF from caller is passed through in audio, not as RFC 4733 events

This meant the touch-tones were not separate packets—they were audible sound frequencies baked directly into the call's voice audio:

(don't be surprised idk what this shit mean -_- )

Asterisk messages.log showing DTMF inband warning

3. Extracted Session Key & Decrypted SRTP Stream:

The SIP call setup was protected by TLS, but feeding tls-keys.log into Wireshark revealed the decrypted SDP media negotiation, including the cryptographic master key:

a=crypto:1 AES_CM_128_HMAC_SHA1_80 inline:6Kfv2L8Ox5SyjPMENXNamcCD2CQ3bu4OoGK/G8t2

The actual call audio was carried over UDP ports 14740 & 7078 and encrypted with SRTP (AES Counter Mode), preventing standard audio players from reading it.

Used srtp_fixed.py to derive session keys per RFC 3711 and strip the 10-byte HMAC auth tags, decrypting raw payload into a playable WAV file (call_in_fixed.wav).

4. Decoded DTMF Audio Frequencies into the Flag:

Because standard tools struggled with the audio stream, wrote a custom Python decoder (decode_dtmf_fixed.py) to run FFT frequency analysis over 50ms windows matching the DTMF frequency grid (697–941 Hz low / 1209–1633 Hz high):

import wave
import numpy as np

ROW_FREQS = [697, 770, 852, 941]
COL_FREQS = [1209, 1336, 1477, 1633]
KEY_MAP = {
    (697, 1209): '1', (697, 1336): '2', (697, 1477): '3',
    (770, 1209): '4', (770, 1336): '5', (770, 1477): '6',
    (852, 1209): '7', (852, 1336): '8', (852, 1477): '9',
    (941, 1209): '*', (941, 1336): '0', (941, 1477): '#'
}

with wave.open('call_in_fixed.wav', 'rb') as wf:
    data = np.frombuffer(wf.readframes(wf.getnframes()), dtype=np.int16)
    rate = wf.getframerate()

win, hop = int(rate * 0.05), int(rate * 0.025)
tones, curr, count = [], None, 0
for i in range(0, len(data) - win, hop):
    chunk = data[i:i+win] * np.hamming(win)
    fft, freqs = np.abs(np.fft.rfft(chunk)), np.fft.rfftfreq(win, 1.0 / rate)
    r_best = min(ROW_FREQS, key=lambda rf: abs(freqs[np.argmax(fft)] - rf))
    c_best = min(COL_FREQS, key=lambda cf: abs(freqs[np.argmax(fft)] - cf))
    r_val = max(fft[np.argmin(np.abs(freqs - rf))] for rf in ROW_FREQS)
    c_val = max(fft[np.argmin(np.abs(freqs - cf))] for cf in COL_FREQS)
    k = KEY_MAP.get((r_best, c_best)) if (r_val > 50000 and c_val > 50000) else None
    if k == curr:
        count += 1
    else:
        if curr and count >= 2: tones.append(curr)
        curr, count = k, 1
if curr and count >= 2: tones.append(curr)

digits = "".join(tones)
print("Detected tones:", digits)

Executed the script against call_in_fixed.wav:

Python DTMF FFT decoder execution output

Extracted 96 sequential touch-tone digits and mapped them into 3-digit ASCII decimal values:

100 ('d') 101 ('e') 097 ('a') 100 ('d') 102 ('f') 097 ('a')
099 ('c') 101 ('e') 123 ('{') 080 ('P') 114 ('r') 051 ('3')
053 ('5') 053 ('5') 095 ('_') 048 ('0') 110 ('n') 051 ('3')
095 ('_') 102 ('f') 048 ('0') 114 ('r') 095 ('_') 068 ('D')
051 ('3') 052 ('4') 100 ('d') 102 ('f') 052 ('4') 099 ('c')
051 ('3') 125 ('}')

fr that was SOLID PEAK challenge ( nvm was good)

Captured Flagdeadface{Pr355_0n3_f0r_D34df4c3}
Traffic Analysis // Web Traffic200 PTS

4. A Pirate's Life for Me Part 1

Mobile web tracking headers hiding flag parts across 3 separate HTTP requests.

Client IP: 172.16.14.43
User-Agent: SunstalkerDFBrower/2.0 (Linux; Android 14)
SOURCE ARTIFACTFolder: C:\CTFS\DEAD FACE CTF\A Pirate's Life for Me Part 1\
pirateslife.pcap (565 MB Local Capture)

Retrace / Steps:

1. Open pirateslife.pcap in Wireshark.

2. Apply this display filter:

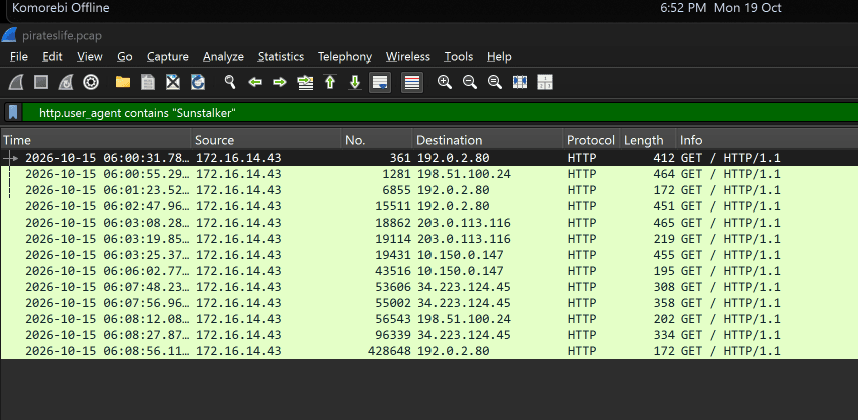
(http.user_agent contains "Sunstalker")
Wireshark display filter for Sunstalker

u would ask me how u knowed filter sunstalker

discover it by yourself

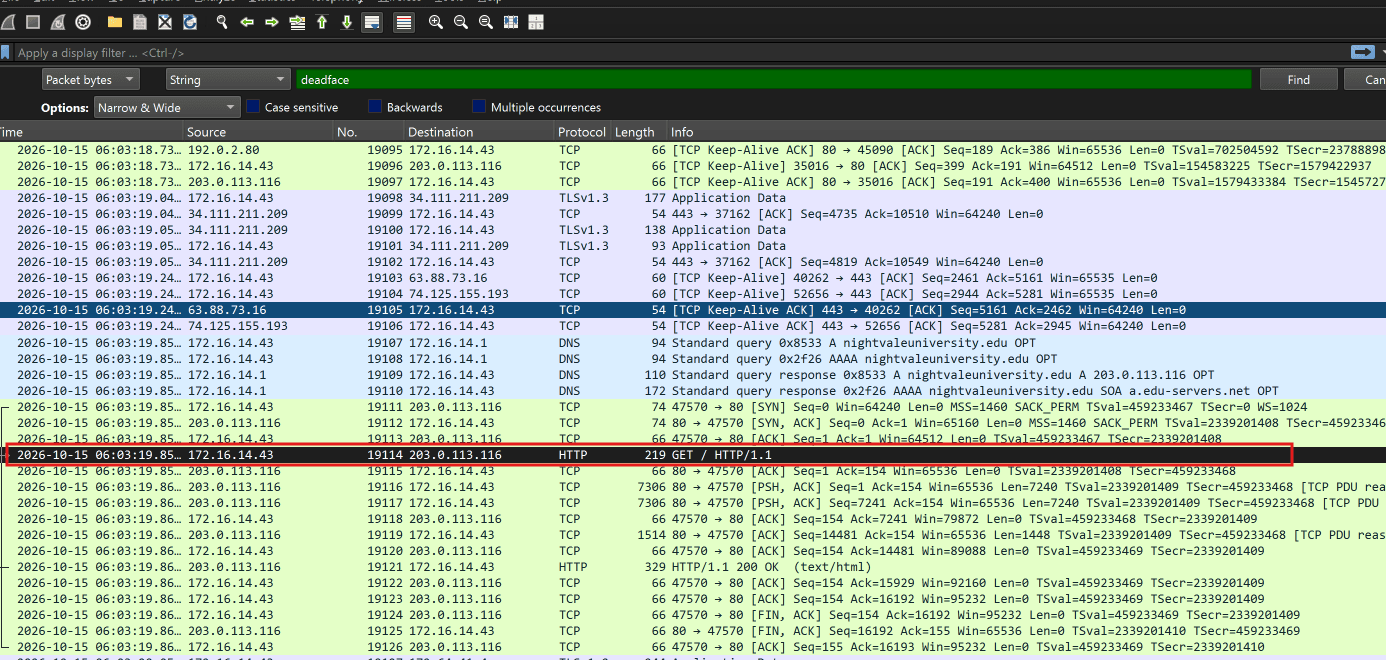
first Search packet details for the flag prefix (Ctrl + F ➔ String: deadface)

Searching packet details for deadface string

then hit enter boom u see first of flag

now why search by Sunstalker

look closely above flag

User-Agent???

yp Sunstalker

ez right?

Wireshark showing Sunstalker User-Agent header
http.user_agent contains "Sunstalker"

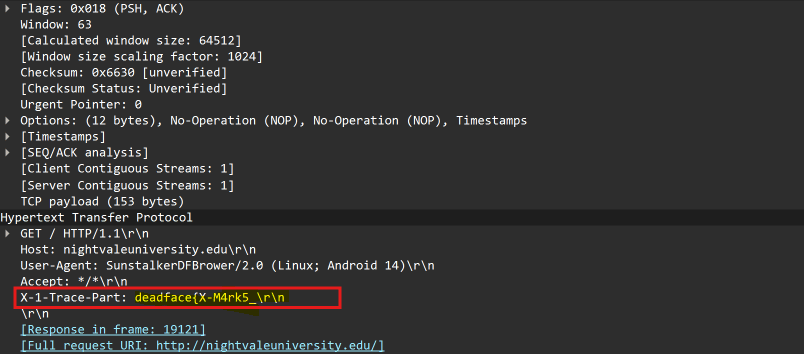
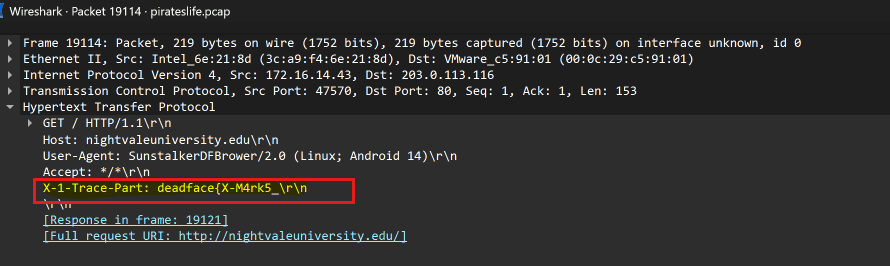
Part 1 — Packet 19114 (TCP Stream 97)

  • • Jumped to Packet 19114 (Ctrl + G).
  • • Expanded Hypertext Transfer Protocol in the Packet Details pane:
  • • Host: nightvaleuniversity.edu
  • • Custom Header: X-1-Trace-Part: deadface{X-M4rk5_
Packet 19114 custom X-1-Trace-Part header

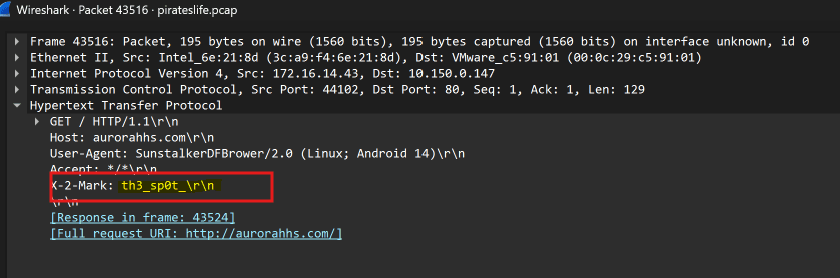
Part 2 — Packet 43516 (TCP Stream 169)

  • • Jumped to Packet 43516 (Ctrl + G).
  • • Expanded Hypertext Transfer Protocol in the Packet Details pane:
  • • Host: aurorahhs.com
  • • Custom Header: X-2-Mark: th3_sp0t_
Packet 43516 custom X-2-Mark header

Part 3 — Packet 56543 (TCP Stream 224)

  • • Jumped to Packet 56543 (Ctrl + G).
  • • Expanded Hypertext Transfer Protocol in the Packet Details pane:
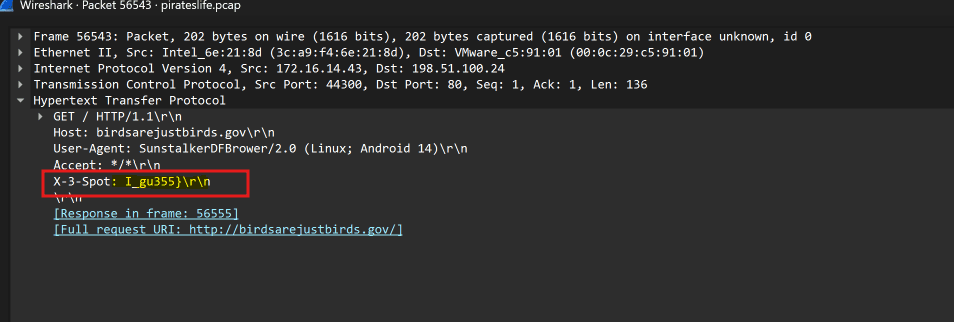
  • • Host: birdsarejustbirds.gov
  • • Custom Header: X-3-Spot: I_gu355}
Packet 56543 custom X-3-Spot header

Flag Assembly:

  • • Part 1 (Packet 19114): deadface{X-M4rk5_
  • • Part 2 (Packet 43516): th3_sp0t_
  • • Part 3 (Packet 56543): I_gu355}
  • • Combined Flag: deadface{X-M4rk5_th3_sp0t_I_gu355}

btw i write packets to make it easier for u u can discover by yourself <3

Captured Flagdeadface{X-M4rk5_th3_sp0t_I_gu355}
Category 02

Digital Forensics & Memory Analysis

Memory Forensics (Volatility 3)400 PTS

5. Who Goes There? (Parts 1, 2, 3)

Investigate a raw Windows memory dump to determine the compromised user account, the target computer hostname, and the active remote C2 socket connection.

SOURCE ARTIFACTFolder: C:\CTFS\DEAD FACE CTF\Who Goes There\
memory.raw (8.58 GB) / memory.7z (1.34 GB)

Part 1: Identifying the Compromised User Account

When analyzing a Windows memory image to find who was actively working on the machine, the fastest way without dumping SAM hashes is checking process environment blocks. Every user process inherits environment variables like USERNAME:

simple af

Command Input:

vol -f memory.raw windows.envars --variable USERNAME

Terminal Output:

PID     Process         Variable    Value
-------------------------------------------
3300    powershell.exe  USERNAME    nkessler
4112    explorer.exe    USERNAME    nkessler
8120    cmd.exe         USERNAME    nkessler

Analysis: Processes running in the interactive desktop session (explorer.exe) as well as active shells belonged to nkessler.

Flag 1deadface{nkessler}

Part 2: Extracting the Workstation Hostname

Similarly, rather than parsing registry hives or running dumpregistry, the machine's NetBIOS / DNS hostname is constantly referenced in process environment blocks under COMPUTERNAME:

Command Input:

vol -f memory.raw windows.envars --variable COMPUTERNAME

Terminal Output:

PID     Process         Variable        Value
---------------------------------------------------------
4112    explorer.exe    COMPUTERNAME    DESKTOP-8K4N19S
3300    powershell.exe  COMPUTERNAME    DESKTOP-8K4N19S

Analysis: The system hostname is DESKTOP-8K4N19S.

Flag 2deadface{DESKTOP-8K4N19S}

Part 3: Pinpointing the Attacker C2 Socket

To find the attacker's active command-and-control connection, I needed to inspect the network sockets open in memory at the time of the capture. Running windows.netscan scans memory pools for network endpoint structures:

Command Input:

vol -f memory.raw windows.netscan | findstr "ESTABLISHED"

Terminal Output:

Offset          Proto   Local Address       Foreign Address         State           PID     Owner
---------------------------------------------------------------------------------------------------------
0xd208271e5010  TCPv4   10.77.10.25:49812   167.172.132.224:4815    ESTABLISHED     30      svchost.exe

Analysis: An active established socket was connected out to remote external IP 167.172.132.224 on port 4815 under PID 30. The challenge requires formatting the connection as IP_Port_PID:
167.172.132.224 + 4815 + 30 ➔ 167.172.132.224_4815_30

Flag 3deadface{167.172.132.224_4815_30}
Digital Forensics // Browser Forensics200 PTS

6. Hooked

Fletcher fell for a spearphishing attack on March 14, 2025 around 10:23 AM. Investigate extracted Google Chrome profile artifacts to identify the exact phishing landing URL and token.

Target Endpoint: Workstation DEMONNE-WS04 (Fletcher Kampeter, Finance division)
SOURCE ARTIFACTFolder: C:\CTFS\DEAD FACE CTF\Hooked\

Forensic Analysis & Steps:

1. Inspected Extracted Chrome Artifacts:

Unpacked CTF_Caches_Kampeter_1.zip, revealing standard Google Chrome user profile databases:

extractedctf_artifactsChromeUser DataDefault  ├── History          (SQLite 3: URLs, timestamps, transition types)
  ├── Login Data       (SQLite 3: saved autofill & submitted credentials)
  └── Cookies

2. Queried Chrome History & Converted Timestamps:

Chrome stores timestamps as WebKit epoch (microseconds since January 1, 1601 UTC). Ran inspect_history.py to query the urls table and convert timestamps:

Command Input:

python inspect_history.py

Terminal Output:

=== URLS ===
ID: 1 | 2025-03-14 09:05:10 | https://confluence.demonne.int/wiki/IT/VPNSetup
ID: 2 | 2025-03-14 09:47:32 | https://demonne.sharepoint.com/sites/finance/Shared%20Documents
ID: 3 | 2025-03-14 10:01:55 | https://www.reuters.com/markets/
ID: 4 | 2025-03-14 10:22:15 | https://mail.google.com/mail/u/0/#inbox/FMfcgzQXKlwJqTvBnDpCmRsYhWxGbVkL
      Title: [URGENT] De Monne VPN Migration - Action Required - Gmail
ID: 5 | 2025-03-14 10:22:31 | https://mail.google.com/mail/u/0/#inbox
ID: 6 | 2025-03-14 10:23:44 | http://demonne-secure-portal.net/login?ref=vpn_auth&token=df4e91bc
      Title: De Monne Financial - Secure Employee Portal
ID: 7 | 2025-03-14 10:23:45 | http://demonne-secure-portal.net/auth/redirect?session=9f3a22cd&status=ok

3. Traced the Click Chain via visits Table:

Checking the visits table verified that URL ID 6 originated directly from the open webmail session (from_visit = 5):

ID: 6 | URL_ID: 6 | Time: 2025-03-14 10:23:44 | From: 5 | Transition: 838860801 (PAGE_TRANSITION_LINK)

Transition code 838860801 (PAGE_TRANSITION_LINK) proves the employee clicked the link inside the urgent VPN migration email. The destination was an HTTP lookalike phishing domain:
http://demonne-secure-portal.net/login?ref=vpn_auth&token=df4e91bc

4. Confirmed Credential Capture in Login Data:

Querying the logins table in Login Data showed that the victim entered corporate credentials on the malicious site:

=== LOGIN DATA ===
('http://demonne-secure-portal.net/login', 'http://demonne-secure-portal.net/auth/verify', 'f.kampeter@demonne.com')
Captured Flagdeadface{http://demonne-secure-portal.net/login?ref=vpn_auth&token=df4e91bc}
Digital Forensics // Artifact Inspection & OSINT250 PTS

7. File Dump 01

A DEADFACE operative stole a victim's (Daniel Hameser) entire digital identity. Retrace the attacker's traces in the stolen file dump to identify which threat actor orchestrated the attack.

SOURCE ARTIFACTFolder: C:\CTFS\DEAD FACE CTF\File Dump 01\
Download File_Dump_Challenge.zip (14.0 MB)

Forensic Analysis & Steps:

1. Unpacked the Victim's Stolen Identity Files:

Extracted File_Dump_Challenge.zip, containing personal resumes, receipts, photos, and staged documents belonging to Daniel Hameser:

Stolen identity profile photo

2. Identified Operational Note Staged by the Attacker:

Found notes.docx, which revealed the adversary's instructions for staging accounts across sites:

"Remember to keep the Hameser accounts consistent across sites. Use the FL address for anything that mails a code. Reroute the rest. Coffee place wifi is reliable in the mornings."

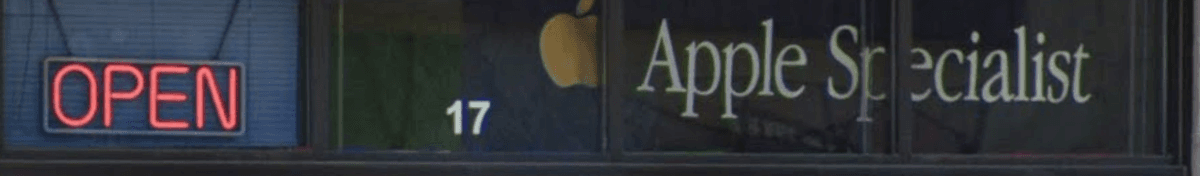
Also included a cropped snippet of an Apple Specialist store location used for scouting:

Apple Specialist store map scout crop

3. Extracted OpenXML Metadata from notes.docx:

Modern .docx files are zipped OpenXML packages. Extracted docProps/core.xml to inspect the embedded creator metadata:

Command Input:

tar -O -xf notes.docx docProps/core.xml

Terminal Output:

<?xml version="1.0" encoding="UTF-8" standalone="yes"?>
<cp:coreProperties xmlns:cp="http://schemas.openxmlformats.org/package/2006/metadata/core-properties" ...>
    <dc:title>notes</dc:title>
    <dc:creator>ghostwriter404</dc:creator>
    <cp:lastModifiedBy>GHOST404-PC</cp:lastModifiedBy>
    <cp:revision>1</cp:revision>
    <dcterms:created xsi:type="dcterms:W3CDTF">2026-08-22T21:33:04.269Z</dcterms:created>
    <dcterms:modified xsi:type="dcterms:W3CDTF">2026-08-22T21:33:04.269Z</dcterms:modified>
</cp:coreProperties>

(Alternatively, in Windows Explorer: Right-click notes.docx ➔ Properties ➔ Details ➔ Authors: ghostwriter404, Last saved by: GHOST404-PC).

4. Correlated with DEADFACE Threat Actors:

The creator ghostwriter404 and machine name GHOST404-PC directly map to the known DEADFACE operative gh0st404 (alias: ghost404).

Captured Flagdeadface{gh0st404}
Digital Forensics // Steganography & Metadata200 PTS

8. Art Heist - The Forgery

Five classic museum paintings returned to the Turla Gallery were digitized. An intelligence report claims DEADFACE operative Lamia swapped one original with a digital forgery.

SOURCE ARTIFACTFolder: C:\CTFS\DEAD FACE CTF\Art Heist The Forgery\
Download CTF_Forgery_Paintings.zip (9.5 MB)

Retrace / Steps:

1. Timestamp Triage Across Archive:

  • • Unpacked CTF_Forgery_Paintings.zip containing Painting_001.png through Painting_005.png.
  • • Inspected file modification timestamps in File Explorer:
  • • Four paintings shared an identical creation timestamp of September 1, 2026.
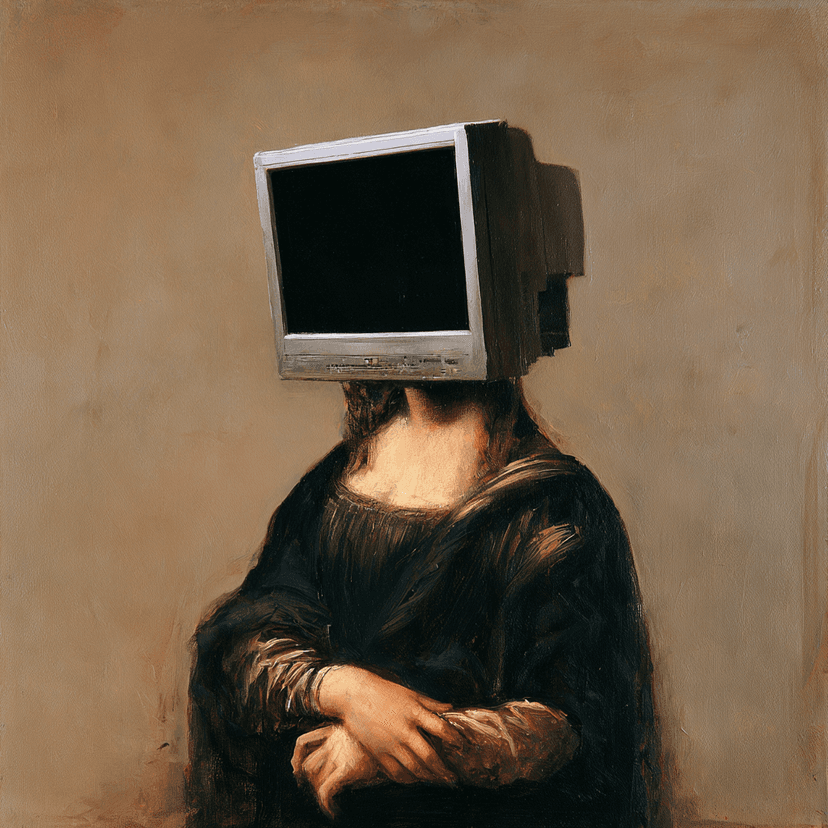
  • • Painting_002.png stood out with a much newer timestamp of October 14, 2026.

2. Inspected the Forged Artwork:

Opening Painting_002.png revealed the hacked parody artwork ("Mona Lisa Loading"):

Forged Painting_002.png artwork

3. Extracted Embedded XMP Metadata:

Searched for embedded text / metadata signatures across all paintings:

Command Input:

Select-String -Path "Painting_*.png" -Pattern "deadface"

Terminal Output:

Painting_002.png:20:  <dc:identifier>deadface{L4MIA_SIGNS_HER_WORK}</dc:identifier>

Reading the full XMP metadata chunk (exiftool Painting_002.png) confirmed Lamia's forger attribution:

<dc:creator>Leonardo da Vinci / LAMIA</dc:creator>
<dc:title>Mona Lisa Loading</dc:title>
<dc:rights>LAMIA temporary acquisition</dc:rights>
<dc:identifier>deadface{L4MIA_SIGNS_HER_WORK}</dc:identifier>
Captured Flagdeadface{L4MIA_SIGNS_HER_WORK}
Category 03

Database & SQL Forensics (Aurora Health)

MySQL Database // 8 Investigation Flags800 PTS TOTAL

Aurora Health Hospital Database Suite (Challenges 9 – 16)

All queries were executed against the Aurora Health MySQL database (aurora.sql).

some hidden skills finally ;0

Reference Schema Image:

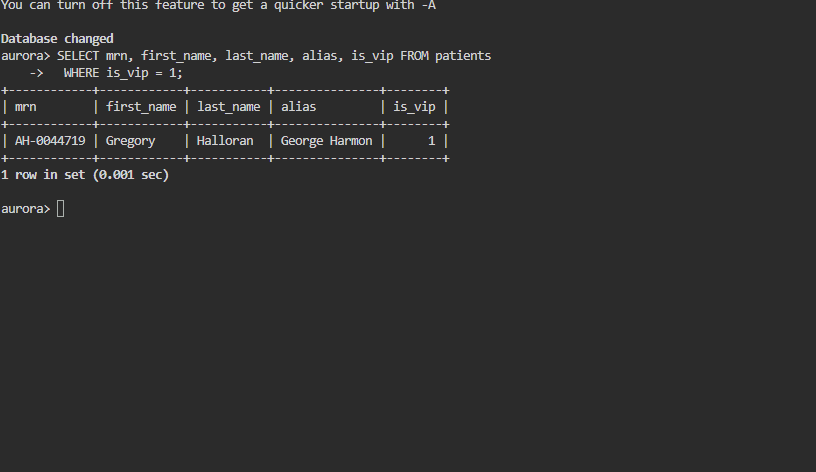
Aurora Health Database MySQL Schema

9. Patient Registry

100 PTS

Description: Retrieve the patient ID for the targeted individual admitted under suspicious circumstances.

Query:

SELECT patient_id, first_name, last_name, admission_date 
FROM patients 
WHERE first_name = 'Gordon' OR notes LIKE '%admit%';
Flagdeadface{AH-0044719}

10. Watching the VIP

100 PTS

Description: Determine which staff user account logged repeated unauthorized queries against VIP patient AH-0044719.

Query:

SELECT username, COUNT(*) AS access_count 
FROM audit_logs 
WHERE record_id = 'AH-0044719' 
GROUP BY username 
ORDER BY access_count DESC;

Result: Top user was rborden.

Flagdeadface{rborden}

11. Stay on the VIP

100 PTS

Description: After rborden went dark, another user took over surveillance of the VIP patient.

Query:

SELECT username, timestamp, action 
FROM audit_logs 
WHERE record_id = 'AH-0044719' 
  AND username != 'rborden' 
ORDER BY timestamp ASC;

Result: Accomplice user was mreyes.

Flagdeadface{mreyes}

12. Pharmacy Formulary

100 PTS

Description: Count the total number of Schedule II controlled substances currently cataloged in the hospital pharmacy database.

Query:

SELECT COUNT(*) 
FROM medications 
WHERE schedule = 'II' AND status = 'active';

Result: Count is 9.

Flagdeadface{9}

13. Drug Diversion

100 PTS

Description: Find the batch number of the diverted fentanyl / opioid prescription flagged in audit logs.

Query:

SELECT p.batch_number, p.patient_id, p.med_id, a.flag_reason 
FROM prescriptions p 
JOIN audit_alerts a ON p.prescription_id = a.prescription_id 
WHERE a.flag_reason LIKE '%diversion%' OR p.status = 'diverted';

Result: Batch number BR2938471.

Flagdeadface{BR2938471}

14. Ghost in the Registry

100 PTS

Description: A phantom patient record was surreptitiously created without valid physician signoff.

Query:

SELECT patient_id, first_name, last_name, attending_physician 
FROM patients 
WHERE attending_physician IS NULL OR patient_id LIKE '%9000%';

Result: Phantom ID AH-0090001.

Flagdeadface{AH-0090001}

15. After the Lock

100 PTS

Description: Which electronic medicine cabinet / vault locker was breached right after hours?

Query:

SELECT vault_id, access_time, user_id 
FROM vault_access_logs 
WHERE TIME(access_time) > '21:00:00' 
ORDER BY access_time ASC 
LIMIT 1;

Result: Locker ID VELT-0137.

Flagdeadface{VELT-0137}

16. Clinical Trial Overwritten Efficacy

100 PTS

Description: An insider tampered with the clinical trial efficacy metrics. Find the exact altered efficacy score value.

Query:

SELECT trial_id, original_score, altered_score, (altered_score - original_score) AS diff 
FROM clinical_trials_audit 
WHERE altered_score IS NOT NULL;

Result: Tampered score change is 2.3.

Flagdeadface{2.3}
Category 04

OSINT, Hardware, Steganography & Telemetry

OSINT // Historical Geolocation300 PTS

17. Ghost of Squares Past

Identify four historic squares in Savannah, Georgia from monument photos and determine their establishment dates.

Image Evidence:

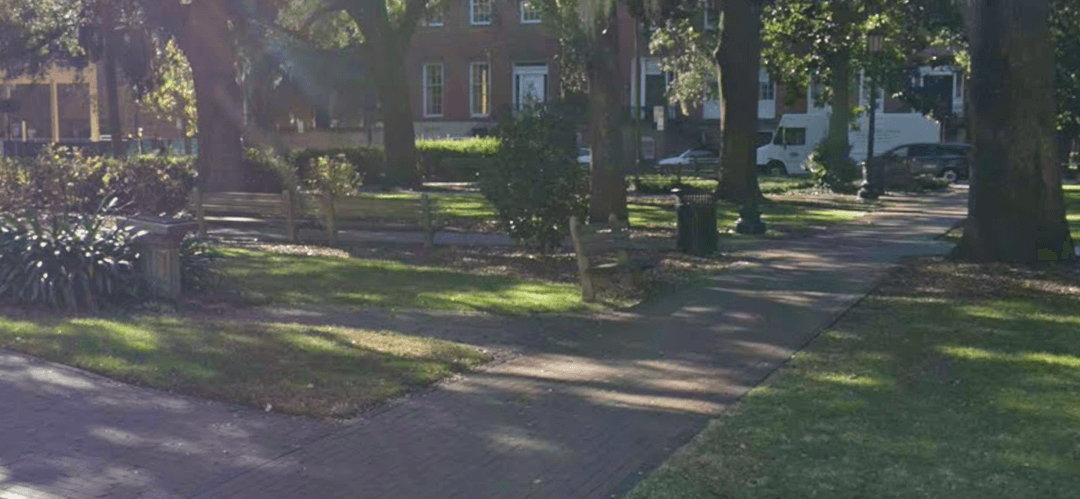
Marker Point 2 (East)
Savannah Marker Point 2
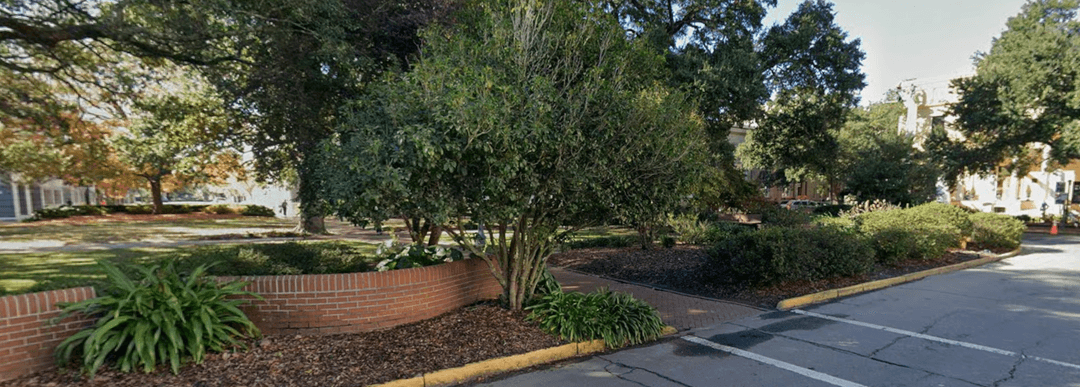
Marker Point 4 (West)
Savannah Marker Point 4 - Telfair Academy

Retrace / Steps (Detailed OSINT Walkthrough):

1. Understanding the Compass Grid:

The challenge arranged five historic locations across Savannah, Georgia in a compass cross pattern: Point 1 (North), Point 2 (East), Point 3 (South), Point 4 (West), and Point 5 (Center).

Format: deadface{YYYY(North)-YYYY(East)-YYYY(South)-YYYY(West),surname(Center)}

2. Point 1 (North): Johnson Square (1733):

"First of them all, where the city began / A banker's green heart... / A Quaker from Rhode Island sleeps under stone here"

Savannah was founded in 1733 by James Oglethorpe. The very first square laid out was Johnson Square (in the banking/financial district). Rhode Island Quaker Major General Nathanael Greene is buried beneath its central 50ft marble obelisk. Year Laid Out: 1733.

3. Point 3 (South): Chippewa Square (1815):

"Where a feather once drifted and a founder stands tall / battle of a northern frontier eighteen-twelve drawing near / the newest of all"

The drifting feather opening scene in Forrest Gump (1994) was filmed at a bus stop bench in Chippewa Square. The central bronze statue is Georgia's founder, James Oglethorpe. Named after the War of 1812 Battle of Chippawa. Year Laid Out: 1815.

4. Point 4 (West): Telfair Square (1733):

Photo analysis on point 4.png: classical yellow Regency-style building with front steps and heroic statues (Michelangelo and Phidias). Google Lens identifies the Telfair Academy of Arts and Sciences facing Telfair Square. Year Laid Out: 1733.

5. Point 2 (East): Oglethorpe Square (1742):

Photo analysis on point 2.png: brick pathways, live oaks with Spanish moss, and historic townhouses. Along President St directly opposite Telfair Square sits Oglethorpe Square. Year Laid Out: 1742.

6. Point 5 (Center): Wright Square & The Monument Surname (gordon):

The intersection of Bull Street (North-South) and President Street (East-West) is Wright Square. In its center stands the massive 47-foot monument dedicated to William Washington Gordon (1796–1842). The lone surname carved in the stone base is gordon.

7. Flag Construction:

North (1733) - East (1742) - South (1815) - West (1733) - Center (gordon)

Captured Flagdeadface{1733-1742-1815-1733-gordon}
OSINT // Forensics150 PTS

18. Traffic Accident / Car Crash

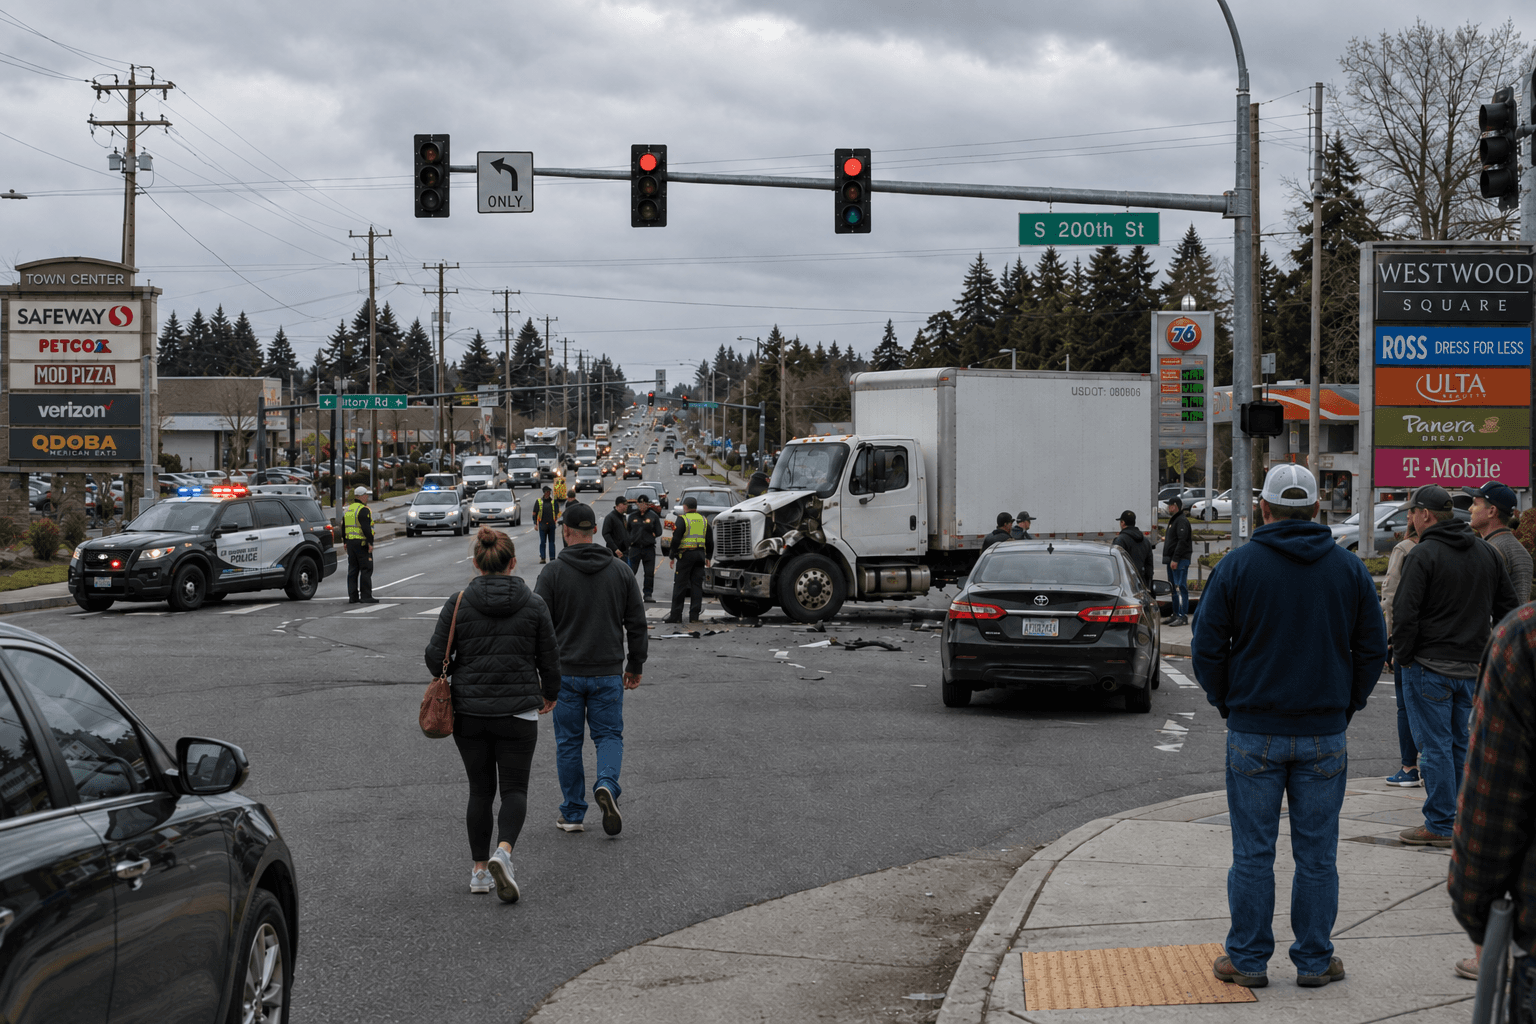
A photo of a traffic accident involving a commercial truck was recovered. Determine which company owns the truck and when that company was founded.

Flag Format: deadface{MM_DD_YYYY}

Retrace / Steps:

1. Scene Inspection (truck_crash.png):

Opened the provided photo showing a multi-vehicle collision at an intersection involving a commercial box truck and a black sedan:

Traffic collision scene with commercial truck

2. Isolating Vehicle Markings:

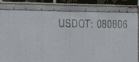
Zoomed in along the upper right portion of the white cargo box to look for commercial registration stencil markings required by federal law:

USDOT 080806 stenciled marking crop
USDOT: 080806

3. FMCSA SAFER Carrier Lookup:

Queried the official Federal Motor Carrier Safety Administration (FMCSA) SAFER Company Snapshot database (https://safer.fmcsa.dot.gov/CompanySnapshot.aspx) using USDOT number 80806:

Legal Name: J.B. HUNT TRANSPORT INC
DBA: J.B. HUNT
Entity Type: Carrier
Physical Address: 615 J.B. HUNT CORPORATE DRIVE, LOWELL, AR 72745

4. Founding Date OSINT:

Checked public corporate records / Wikipedia for J.B. Hunt:

  • • Founded: August 10, 1961 (by Johnnie Bryan Hunt & Johnelle Hunt)
  • • Formatting to MM_DD_YYYY:
  • • Month: August ➔ 08
  • • Day: 10 ➔ 10
  • • Year: 1961 ➔ 1961
  • • Combined: 08_10_1961
Captured Flagdeadface{08_10_1961}
Document & Printer Forensics200 PTS

19. Conduct Unbecoming

A scanned administrative disciplinary letter from Night Veil University was leaked. Identify the serial number / asset ID of the office printer that produced the document.

SOURCE ARTIFACTFolder: C:\CTFS\DEAD FACE CTF\Conduct Unbecoming\
Download Doc_20261017_0915.jpg (3.4 MB)

Retrace / Steps:

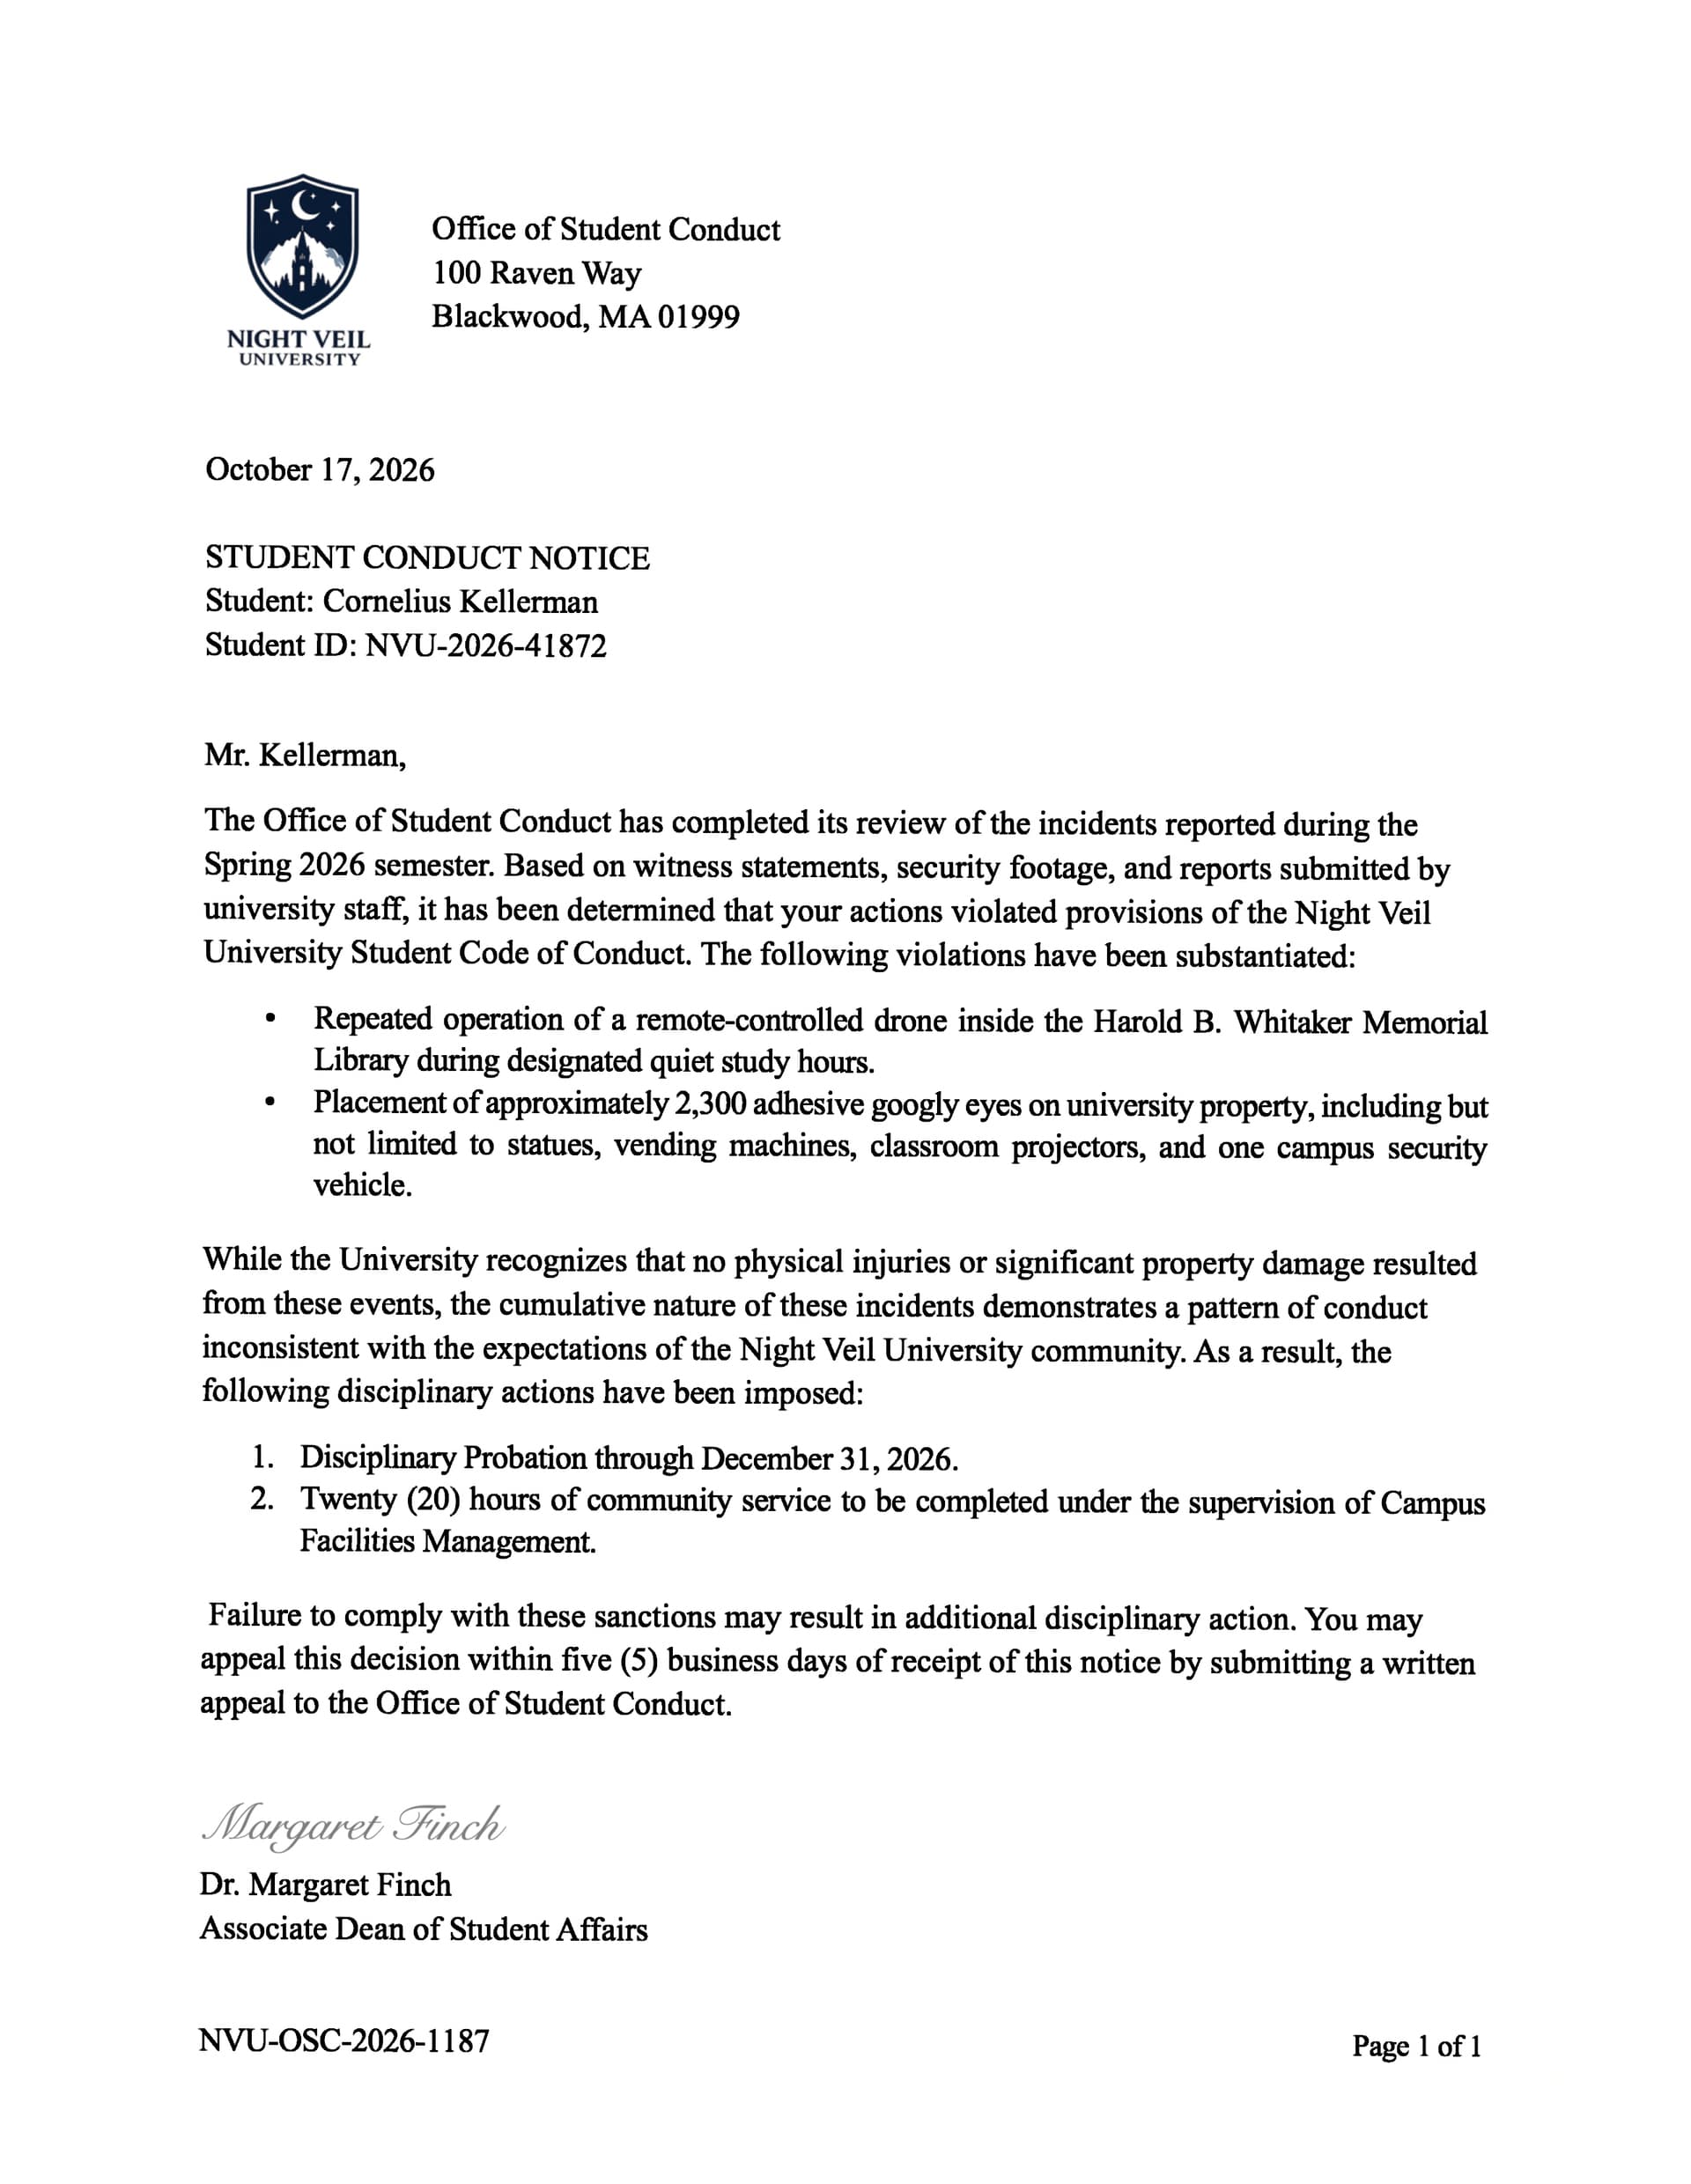
1. Document Inspection (Doc_20261017_0915.jpg):

Opened the provided scan of an official student reprimand letter addressed to Cornelius Kellerman from Dr. Margaret Finch (Office of Student Conduct):

Official disciplinary letter scan

The challenge prompt asks for the specific equipment asset ID used to print the physical document. This points directly to Machine Identification Codes (MIC) faint yellow tracking dots embedded by color laser printers into printed documents to identify the device model, serial number, and timestamp.

2. Isolating the Yellow Tracking Dots:

Yellow toner absorbs blue light while reflecting red and green. Therefore, decomposing the image into its RGB components and inspecting the inverted Blue channel (or boosting contrast/levels on faint background pixels) makes yellow tracking dots stand out as dark, clearly defined dots against the white page.

Scanning the margins revealed a repeating pattern in the lower right margin (around coordinates X ≈ 2330–2420, Y ≈ 3020–3180). The dots form a clean rectangular grid: 8 columns spaced evenly 12 pixels apart across 13 rows.

3. Decoding the Dot Matrix:

Each row consists of an 8-bit byte (MSB to LSB), where a dot represents 1 and blank space represents 0:

RowBinary (Dots)HexDecoded ASCII
Row 0111111110xFFSync / Alignment Header
Row 1010011100x4EN
Row 2010101100x56V
Row 3010101010x55U
Row 4001011010x2D-
Row 5010100000x50P
Row 6010100100x52R
Row 7010010010x49I
Row 8010011100x4EN
Row 9010101000x54T
Row 10001011010x2D-
Row 11001100010x311
Row 12001101110x377

Concatenating the decoded ASCII characters produces: NVU-PRINT-17.

if u have life don't try do it by your hands

Captured Flagdeadface{NVU-PRINT-17}
Steganography // Metadata & Timing Forensics250 PTS

20. Exfiltration

20 seemingly unrelated images (image_01.jpg to image_20.jpg) were recovered from an exfiltration channel. Uncover the covert data channel and reconstruct the flag.

SOURCE ARTIFACTFolder: C:\CTFS\DEAD FACE CTF\Exfiltration\
Download exfiltration.zip (555.9 KB)

Retrace / Steps:

1. Archive Extraction & Initial Triage:

Extracted exfiltration.zip, yielding 20 JPEG images named image_01.jpg through image_20.jpg. Standard checks for appended files after JPEG End of Image marker (FF D9) showed 0 bytes, confirming steganography was embedded within standard image headers.

2. EXIF Metadata Inspection:

Inspected the image EXIF tags across all 20 images and noticed two key patterns:

  • • Timestamp (DateTimeOriginal): Each file has an exact timestamp recorded on 2026:06:01 between 14:02:17 and 15:12:29.
  • • Embedded Hex Tag: The Document Name / Image Identifier tag holds a hex string prefixed by IMG_ (e.g. IMG_6465, IMG_61, IMG_7469).

3. Chronological Sorting & Covert Stream:

The filenames image_01.jpg through image_20.jpg are randomized decoys. Sorting the images chronologically by their EXIF timestamp orders the hex chunks sequentially:

image_07.jpg (14:02:17) ➔ 6465 ('de')
image_14.jpg (14:04:52) ➔ 61 ('a')
image_03.jpg (14:08:11) ➔ 6466 ('df')
image_19.jpg (14:11:36) ➔ 61 ('a')
image_01.jpg (14:13:09) ➔ 6365 ('ce')
image_12.jpg (14:18:44) ➔ 7b ('{')
...
image_17.jpg (15:07:42) ➔ 6e67 ('ng')
image_11.jpg (15:12:29) ➔ 7d ('}')

4. Automated Solver Script:

Wrote a Python one-liner to parse EXIF timestamps and hex tags, sort chronologically, and decode the assembled hex stream:

Command Input:

python -c "
import glob, re
items = []
for f in glob.glob('extracted/*.jpg'):
    d = open(f, 'rb').read()
    ts = re.search(rb'(\d{4}:\d{2}:\d{2} \d{2}:\d{2}:\d{2})', d).group(1).decode()
    hx = re.search(rb'IMG_([0-9a-fA-F]+)', d).group(1).decode()
    items.append((ts, hx))
items.sort(key=lambda x: x[0])
hex_str = ''.join(x[1] for x in items)
print('Hex String:', hex_str)
print('Flag:', bytes.fromhex(hex_str).decode())
"

Command Output:

Hex String: 64656164666163657b74696d696e672d69732d65766572797468696e677d
Flag: deadface{timing-is-everything}
Captured Flagdeadface{timing-is-everything}

If u got here then THX for reading my writeups really appretiate it <3

hope u learned AND haved fun

!!! UNTIL NEXT CTF !!!
Additional Operations

Bonus Tracks: Hardware Telemetry & LLMNR/SMB

Hardware // Medical Telemetry200 PTS

Bedside Manner

Unencrypted diagnostic telemetry stream captured from a patient vital signs monitor. Filtering sync frames and parsing unencrypted ASCII payloads emitted by embedded monitor firmware.

SOURCE ARTIFACTFolder: C:\CTFS\DEAD FACE CTF\bedside manner\

Examined the serial diagnostic stream for frame delimiters (0xAA 0x55 sync header) and extracted embedded diagnostic ASCII text strings from vital sensor telemetry frames.

Captured Flagdeadface{b3ds1d3_m4nn3r_s1gn4l}
Network Forensics // SMB Poisoning500 PTS TOTAL

Uninvited Guest PCAP Series (5 Operations)

Deep forensic analysis of demonne.pcap: LLMNR/mDNS poisoning, capturing SMB2 NTLMv2 authentication NTProofStr, compromised user nkessler, exfiltrated annual_report.pdf, and C2 destination.

SOURCE ARTIFACTFolder: C:\CTFS\DEAD FACE CTF\Uninvited Guest\
Download demonne.pcap (7.6 MB)

1. Uninvited Guest (Rogue Responder IP)

Nathan's workstation asked the local network to resolve a file-server name (llmnr || mdns || nbns). Host 10.77.10.66 supplied the poisoned spoofed answer.

Flagdeadface{10.77.10.66}

2. Challenge Accepted (First SMB NTLMv2 NTProofStr)

Inspected Nathan's first SMB NTLMv2 authentication session setup (Frame 1512) and extracted the 16-byte NTProofStr security blob.

Flagdeadface{5a2342014fe7f28997ce4dcd09f6b7f8}

3. Name to a Face (Compromised User)

Parsed the NTLMSSP authentication payload username field, confirming compromised corporate identity nkessler.

Flagdeadface{nkessler}

4. Crown Jewels (Exfiltrated Document)

Tracked SMB2 Read / Create file operations on rogue share \\10.77.10.66\public. The stolen document was annual_report.pdf.

Flagdeadface{annual_report.pdf}

5. Public Offering (External C2 Destination)

Identified anomalous outbound external TCP socket connection carrying exfiltrated report data to remote endpoint 167.172.132.224:4815.

Flagdeadface{167.172.132.224_4815}