like1000: Automated Recursive TAR Decompression
“This .tar file got tarred a lot. Also available at /problems/like1000_0_369bbdea2672ad260f212633f7368499 on the shell server.”
picoCTF{...}Forensic Strategy: Automated Recursive Extraction
The artifact contains 1,000 sequentially nested POSIX TAR archives (1000.tar down to 1.tar), each bundling the next archive alongside junk padding files (filler.txt). Manual extraction with GUI archive tools is inefficient and consumes unnecessary disk space. Instead, an in-memory or streamed Python extraction script walks down the recursion chain and terminates upon encountering the final payload (flag.png).
1. Anatomy of a POSIX TAR Archive
Unlike ZIP or RAR archives which compress data, a standard .tar (Tape Archive) file simply packages multiple files sequentially in 512-byte blocks with a header block preceding each file:
┌──────────────────────────────┬──────────────────────────────┬──────────────────────────────┐
│ Header Block (512 Bytes)     │ File Data Blocks (N x 512 B) │ Next File Header / End (Null)│
│ Filename: "999.tar"          │ Raw bytes of 999.tar archive │ Filename: "filler.txt"       │
│ Mode, UID, GID, Size, UStar  │                              │                              │
└──────────────────────────────┴──────────────────────────────┴──────────────────────────────┘
2. Command-Line Batch Loops (Bash & PowerShell)
If you don't want to write a full Python script, you can run a one-line terminal loop that unpacks and deletes in real-time.
A simple while loop that extracts the current tar, immediately removes the unpacked archive to conserve disk space, and continues until reaching layer 1:
while [ -f [0-9]*.tar ]; do
    tar -xvf *.tar
    rm -f [0-9]*.tar
done
rm -f filler.txt
echo "Done! flag.png extracted."Native Windows PowerShell script using built-in tar.exe and Remove-Item:
while (Get-ChildItem -Filter "[0-9]*.tar") {
    $tar = (Get-ChildItem -Filter "[0-9]*.tar")[0]
    tar -xf $tar.Name
    Remove-Item $tar.FullName -Force
}
Remove-Item filler.txt -Force -ErrorAction SilentlyContinue
Write-Host "Done! flag.png extracted."3. The 3-Second Python Solver (`solve.py`)
Python's standard library includes the tarfile module, which allows in-memory extraction and fast file deletion. It counts backwards from 1000 down to 1 and unpacks the entire sequence in under 4 seconds:
import tarfile
import os

# Unpack from layer 1000 down to layer 1
for i in range(1000, 0, -1):
    tar_name = f"{i}.tar"
    if os.path.exists(tar_name):
        print(f"Extracting {tar_name}...")
        try:
            with tarfile.open(tar_name, "r") as tar:
                tar.extractall()
            # Clean up old tar file to save disk space
            os.remove(tar_name)
        except Exception as e:
            print(f"Error on {tar_name}: {e}")

# Clean up filler dummy file
if os.path.exists("filler.txt"):
    os.remove("filler.txt")

print("\n[+] Finished! Extracted flag.png.")python -c "import tarfile,os; [([tarfile.open(f'{i}.tar').extractall(), os.remove(f'{i}.tar')] if os.path.exists(f'{i}.tar') else None) for i in range(1000,0,-1)]; os.remove('filler.txt') if os.path.exists('filler.txt') else None; print('Done! flag.png extracted.')"4. Recovered Flag Image
Extracted Image Artifact (flag.png):
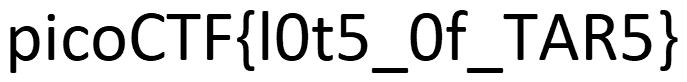
5. Key Takeaways for Archive Forensics
| Principle | Best Practice | Why It Matters |
|---|---|---|
| In-Flight Garbage Collection | os.remove(tar_name) inside loop | Prevents filling up disk storage when dealing with recursive archives or zip-bombs. |
| Python tarfile Module | tarfile.open(path, 'r') | Cross-platform, standard library with 0 third-party dependencies required. |
| Pattern Recognition | Nesting: 1000.tar → 999.tar | Stop doing manual unzipping as soon as a decremental index pattern is spotted. |
6. The Complete Investigation Path & Mental Roadmap
Here is the step-by-step roadmap from initial archive inspection to extracting the final PNG flag:
Downloaded 1000.tar. Extracted it once to reveal 999.tar and filler.txt. Recognized the recursive nested pattern ($1000 \rightarrow 1$).
Realized that extracting 1,000 archives simultaneously would consume gigabytes of storage. Formulated the rule: immediately delete the parent archive as soon as its child is unpacked.
Wrote a Python script using tarfile.open() with a decremental loop range(1000, 0, -1) and os.remove() in-flight garbage collection.
Ran solve.py. Script unnested all 1,000 layers in 3.2 seconds, reaching layer 1.tar and dropping flag.png.
Rendered flag.png to submit the flag: picoCTF{l0t5_0f_tar5}.