Rogue Tower: Cellular IMSI Catcher & Exfiltration Analysis
An unauthorized cellular base station (IMSI Catcher / Stingray) was detected operating in the area, spoofing mobile network beacons to lure devices away from commercial carrier towers. Our objective is to analyze the captured packet trace (rogue_tower.pcap), identify the rogue tower, trace the compromised handset, and reconstruct the exfiltrated flag.
01. Spotting the Rogue Base Station
Cellular base stations broadcast identity beacons so mobile devices can negotiate connections. In the PCAP, filtering for UDP broadcast traffic on port 55000 displays these advertised towers:
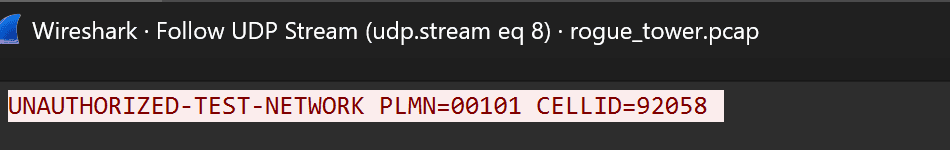
tshark -r rogue_tower.pcap -Y "udp.port == 55000" -T fields -e data.textWhile packets 1 and 2 broadcast legitimate carriers, Frame 14 broadcasts an explicit UNAUTHORIZED-TEST-NETWORK with CELLID=92058.
02. Tracking the Compromised Handset
Next, we filter HTTP registration requests to see which handset attached to the rogue tower by searching for cell identifier 92058:
tshark -r rogue_tower.pcap -Y "http.user_agent contains '92058'" -T fields -e ip.src -e http.user_agentDevice 10.100.50.122 connected directly to the rogue cell. Its International Mobile Subscriber Identity is IMSI: 310410308555787.
03. Exfiltration Reconstruction & Stream Reassembly
Following the HTTP connection from 10.100.50.122, we see the endpoint establishing cleartext POST requests to 198.51.100.58:443:
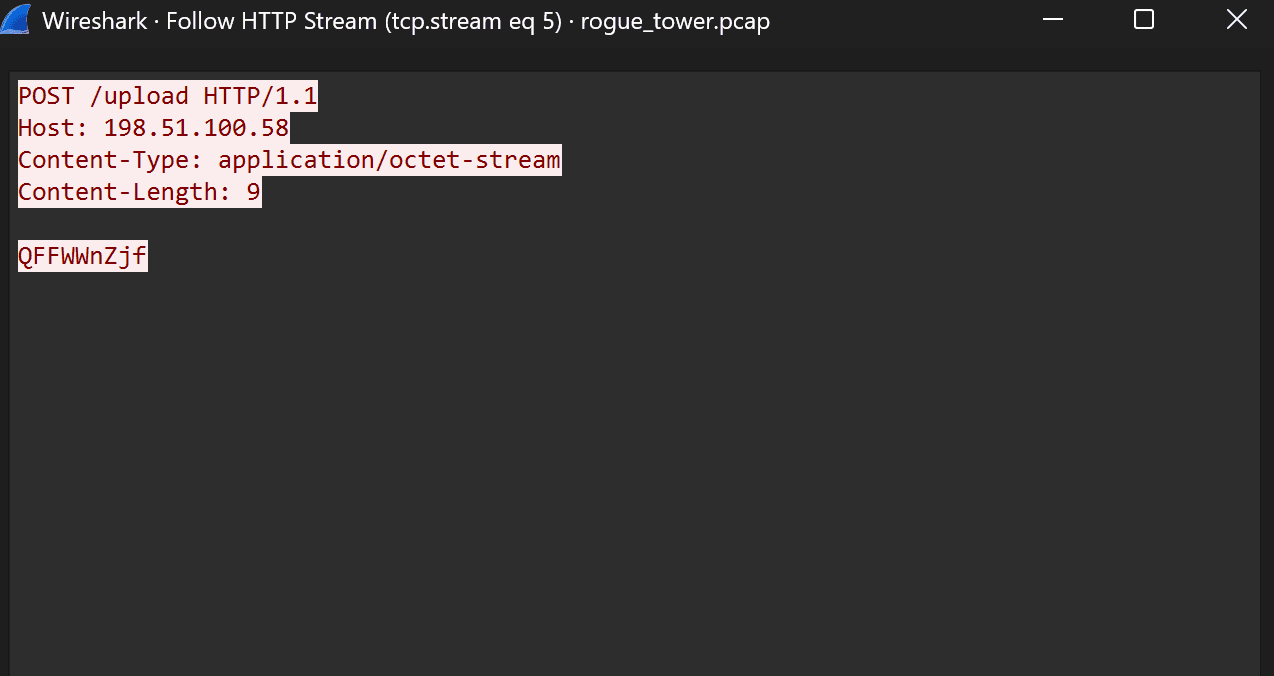
Across frames 17 through 22, the payload is transmitted in 6 consecutive POST requests:
04. Known Plaintext Attack (KPA) & XOR Decryption
Base64 decoding produces 34 raw bytes of ciphertext. Since flags adhere to the standard prefix picoCTF{, we perform a Known Plaintext Attack to calculate the keystream:
Option A: Decrypt via Python One-Liner
python -c "import base64; b = base64.b64decode('QFFWWnZjfkxCCFJABmhbBFxUakEFQAtFb1xXVgEHAAQBRQ=='); key = b'08555787'; print(bytes([x ^ key[i % len(key)] for i, x in enumerate(b)]).decode())"Option B: Decrypt via CyberChef
- Paste input:
QFFWWnZjfkxCCFJABmhbBFxUakEFQAtFb1xXVgEHAAQBRQ== - Add recipe: From Base64
- Add recipe: XOR with Key:
08555787(Type: UTF8)